Protection overview
BotBlocker lets people in, keeps bots out, and asks a question when it is not sure.
Your site gets much more than visits from people. Search engines crawl it, monitoring tools check it, scanners look for weak spots, and your own server sends requests during updates and scheduled tasks. Some of this traffic is welcome, and some is not. No single rule can always tell them apart.
BotBlocker looks at each request and uses many small signs together. Most real visitors never notice it. Bad bots get a check they cannot pass, or a block. The setting names in this guide match the plugin, so you can move between the guide and the settings screen without guessing.
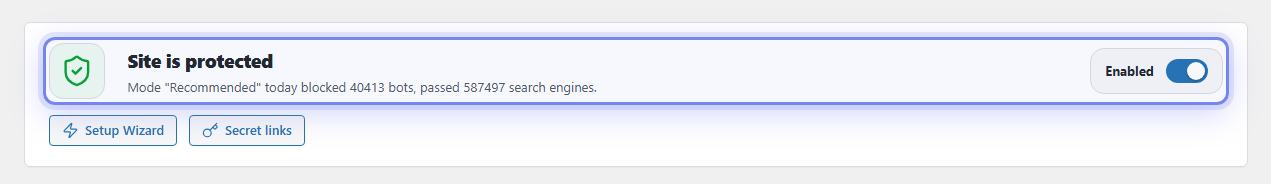
The Protection status panel on the Dashboard. Open it from BotBlocker → Dashboard. Change the protection settings in BotBlocker → Settings.
What BotBlocker does with a visit
BotBlocker looks at each request and chooses one of these outcomes:
- Let it through. The request reaches your site normally. This is what you want for ordinary visitors and for the services your site depends on.
- Ask the visitor to verify access. BotBlocker shows a check page when a request looks unusual but the available signals are not strong enough to block it. After the visitor completes the check, they can continue. This gives uncertain requests a chance to pass without refusing an entire group of visitors because of one clue.
- Refuse the request temporarily. BotBlocker sends an error response and remembers the visitor for a while. The refusal ends on its own. It is not a permanent ban.
- Limit request frequency. Rate limiting measures how many requests come from a visitor or network during a defined time window. When activity exceeds the configured threshold, BotBlocker can require verification or apply a temporary block.
No setting can know a visitor's intention. A privacy tool, company network, mobile network, VPN, unusual browser, or slow connection can look strange even when the person is genuine. Stricter protection always trades some legitimate access for fewer unwanted visits.
Where BotBlocker sits in the request
BotBlocker works during the WordPress loading process, before your theme builds the page a visitor sees. Optional earlier layers can inspect requests even sooner, before the main WordPress flow begins. Read Early phase and MU mode to see where each layer runs and choose the setup that fits your site.
If a setting locks you out, you do not have to edit files or use the database. The Dashboard has a pause switch, and there are emergency recovery links. See Pause protection and Emergency recovery secrets.
Find the page for your problem
| What you notice | Read this |
|---|---|
| You need to know which parts of the site BotBlocker checks, and which requests it leaves alone | Where protection applies |
| Visitors on VPNs, offices, schools, or mobile networks are refused | Network connection types |
| A visitor is unexpectedly shown a check page, or an external service cannot connect | Bot detection signals |
| Visitors using private browsing or an ad blocker are refused | Browser checks |
| A store, form, API, or payment callback stops working | Blocks and responses |
| Tracking links, embedded pages, or search visibility behave differently | Search and referrer behavior |
| You want stronger checks for determined automation | Stricter checks |
| Traffic arrives in bursts, or one network floods the site | Rate limiting |
| The same bots come back again and again | Behavioral Analysis (add-on) |
| Blocked addresses should be stopped before WordPress loads | Early Init (add-on) |
What the plugin covers
BotBlocker protects your site from unwanted, abusive and automated activity, and it keeps normal visitors and trusted services working. Traffic decisions are only the first part. The core also covers bot detection, visitor verification, temporary blocks, rate limiting, response controls, account protection, monitoring and recovery.
Some of it runs outside the main WordPress request flow. With the right options or add-ons, BotBlocker can inspect traffic earlier, protect logins and administrator access, set security response headers, enforce HTTPS, manage XML-RPC, scan WordPress files and database content for malware, control scheduled tasks, and send security reports. Each of these is a separate module, so a site turns on only what it needs.
Related sections: account security, services and infrastructure, monitoring and reports, HTTP and site behavior, and advanced and recovery controls. If you install an add-on, read its settings and its guide too: add-ons extend the core with more security and administration features.
What BotBlocker does not replace
BotBlocker is one part of your site security, not all of it. You must still:
- Keep WordPress, your theme, and your plugins up to date.
- Use strong passwords and two-factor authentication for administrators. See Account security overview.
- Give admin access only to people who need it.
- Keep backups, and use hosting that can handle a sudden rush of traffic.
Change one thing at a time
- Keep the starting settings while you learn how visitors use the site.
- Change one related setting at a time, and write down what you changed and why.
- Check reports for normal visitors who were challenged or refused. Read Monitoring overview.
- If legitimate visitors are affected, review the setting responsible and adjust it so their normal visits can continue.
If you are not sure where to start, run the Setup Wizard and select Strong protection. Let it provide the baseline, then enable individual settings only when they match a specific need on your site.
When a real visitor cannot get in
First, check the log. Open BotBlocker → Reports, search for the visitor's IP address or the page they tried, and read the decision sentence on the row. It tells you why BotBlocker stopped the visitor and which settings page to open next. See Investigating one visitor, step by step.
Then decide what the visitor sees:
- A check appears. The rule is asking for proof. Confirm the visitor can complete the check and that the chosen CAPTCHA works. See CAPTCHA.
- The visitor is refused immediately. Use the decision sentence in the log to find the rule that caused it, then read the page that owns that rule.
- Only one integration fails. Check Blocks and responses, then Responses and API access for preflight requests and status codes.
- Only visitors on VPNs, mobile networks, or work networks fail. Review Network connection types before changing browser checks.
- Administrators or scheduled work fail. Review Internal site connections and the selected Security Check Mode.
- Everyone is locked out. Use the Dashboard pause switch, or the links in Emergency recovery secrets.
Change the narrowest related setting. Switching off all protection hides the cause and leaves the original problem unresolved.